- New
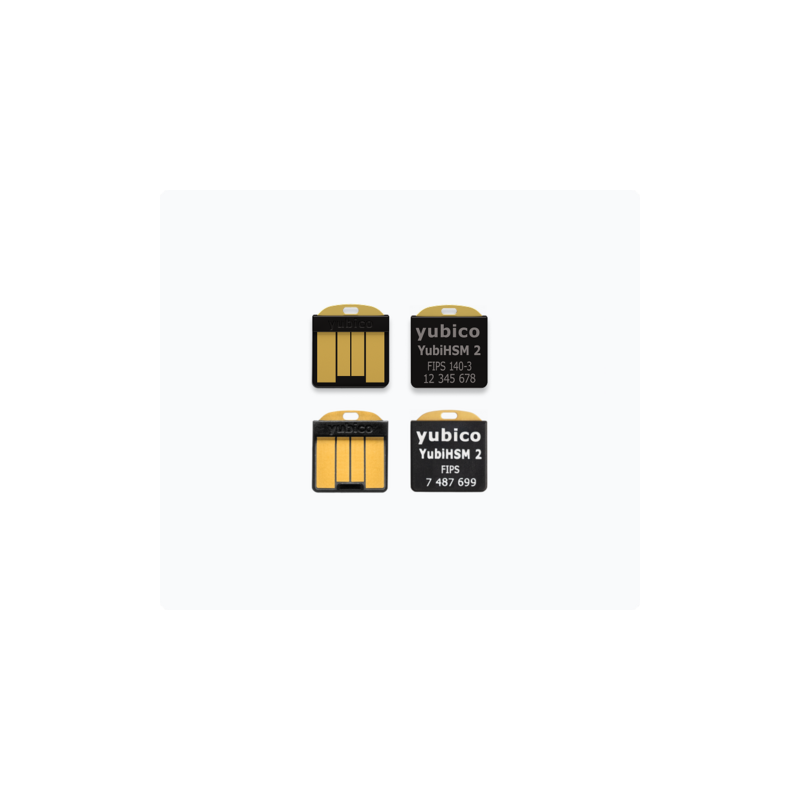
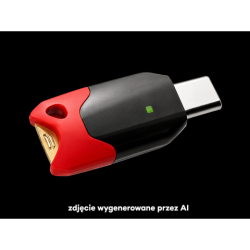
The YubiHSM 2 is a compact hardware security module (HSM) from Yubico designed for securely generating, storing, and using cryptographic keys. The device isolates private keys from the operating system and server applications, enabling cryptographic operations without the need to expose key material outside the protected hardware environment.
Yubico YubiHSM 2 / YubiHSM 2 FIPS – Hardware Security Module (HSM)
The YubiHSM 2 is a compact hardware security module (HSM) from Yubico designed for securely generating, storing, and using cryptographic keys. The device isolates private keys from the operating system and server applications, enabling cryptographic operations without the need to expose key material outside the protected hardware environment.
The YubiHSM 2 is designed primarily for securing server infrastructure, PKI (Public Key Infrastructure) systems, CA certificate authorities, code signing, applications using cryptographic keys, IoT environments, and cloud and multi-cloud systems.
One of the most common applications is securing Certificate Authority (CA) private keys, including infrastructures based on Microsoft Active Directory Certificate Services (AD CS). The HSM can store the CA key and perform cryptographic signing operations without exporting the private key to the server's memory.
The device communicates via USB-A and, thanks to the YubiHSM software, can also be shared with applications running on other servers over the network. Standard integration mechanisms such as PKCS#11, Microsoft CNG/KSP, and native Yubico libraries are supported.
Key Features
HSM-class hardware security module
Secure cryptographic key generation
Hardware-based private key storage
Performance of cryptographic operations without revealing private keys to the host system
Digital signature support
Decryption support
Hash function and HMAC support
Secure export and import of encrypted keys – key wrapping
Secure key backup support
Ability to validate keys generated directly in the HSM
Extensive access control based on roles, domains, and permissions
Up to 16 simultaneous sessions/connections
Encrypted and authenticated communication channel between the application and the HSM
Tamper-evident audit logging – a protected operation log enabling tamper detection
Remote management capability
Ability to share the device between applications over the network
PKCS#11 support
Support for native YubiHSM libraries
Microsoft Key Storage Provider – KSP support
Ability Integration with Microsoft Active Directory Certificate Services
Ability to integrate with custom applications via SDK
Supports Bring Your Own Key (BYOK) scenarios
Battery-free
No moving parts
IP68-rated housing
Crush-resistant design
Extra-small Nano format, allowing the device to remain in the server's USB port.
Models/Variants
YubiHSM 2 v2.4
Standard version of the YubiHSM 2
Firmware from the 2.4 family
USB-A connector
Not FIPS 140-3 certified
Full set of cryptographic mechanisms supported by the device
Intended for environments requiring hardware-based cryptographic key protection but not requiring a FIPS certified module
PKCS#11 support
Microsoft KSP support
Support for native Yubico libraries
BYOK support
Support for backup using asymmetric cryptography in the v2.4 generation
GTIN: 5060408465462
Yubico article number: 100846.
YubiHSM 2 FIPS 140-3 v2.4
Certified version of the YubiHSM 2 intended for organizations with regulatory and compliance requirements
FIPS certification 140-3 Security Level 3
NIST CMVP certification: #5302
USB-A connector
Product marked with the physical inscription "FIPS"
FIPS Approved Mode
Only algorithms and services approved by FIPS requirements are available in FIPS mode
Certified module firmware: 2.4.1
PKCS#11 support
Microsoft KSP support
Native Yubico library support
BYOK support
Backup support using asymmetric cryptography
GTIN: 5060408466384
Yubico article number: 101212.
In FIPS Approved Mode, some of the mechanisms available in the standard YubiHSM 2 are disabled. This includes, among others: ECDSA with SHA-1, secp256k1 curve, RSA PKCS#1 v1.5 for decryption, and selected RSA operations using SHA-1.
Software Required for Operation
The YubiHSM 2, unlike a typical YubiKey authenticator, requires a dedicated software layer enabling application communication with the HSM.
The basic software package is the YubiHSM 2 SDK, provided by Yubico. The SDK is available for Windows, macOS, and select Linux distributions.
Depending on the intended use, the following components are installed:
libyubihsm – a core library enabling applications to communicate with the YubiHSM 2
YubiHSM Connector – a service that acts as an intermediary between the USB device and applications; it also allows for sharing the HSM over the network
YubiHSM PKCS#11 Module – a module required by applications integrating with the HSM via the PKCS#11 standard
YubiHSM Key Storage Provider – KSP – a component for Microsoft environments using CNG, including: Microsoft Active Directory Certificate Services
YubiHSM Shell – a CLI tool for device configuration, administration, and diagnostics
YubiHSM Manager – a graphical/utility environment for YubiHSM configuration and provisioning
YubiHSM Auth – a tool for using YubiHSM credentials stored on the YubiKey
YubiHSM Wrap – a tool for preparing encrypted objects for import
python-yubihsm – a library enabling the integration of YubiHSM 2 with Python applications.
Not all of the above components are required. The required set depends on the environment and the application interacting with the HSM.
Direct USB Connection
The application can communicate directly with the YubiHSM 2 via the libyubihsm library.
The yhusb:// USB backend is used.
In this scenario, a separate YubiHSM Connector service is not required.
This solution is suitable when the HSM is physically connected to the same host as the application.
Network connection
YubiHSM Connector required
The Connector communicates with the device via USB
Applications can connect to the Connector via HTTP/HTTPS
The Connector itself does not have access to the decrypted session – a secure session is established cryptographically between the application and the YubiHSM 2
It is possible to share a single device with applications located on different servers.
Microsoft Active Directory Certificate Services
W przypadku wykorzystania YubiHSM 2 z Microsoft AD CS wymagany jest YubiHSM Key Storage Provider (KSP) oraz YubiHSM Connector. KSP integruje urządzenie z Microsoft Cryptography API: Next Generation – CNG.
Network Connection
A YubiHSM Connector is required.
The Connector communicates with the device via USB.
Applications can connect to the Connector via HTTP/HTTPS.
The Connector itself does not have access to the decrypted session – a secure session is established cryptographically between the application and the YubiHSM 2.
It is possible to share a single device with applications located on different servers.
Microsoft Active Directory Certificate Services
When using YubiHSM 2 with Microsoft AD CS, the YubiHSM Key Storage Provider (KSP) and the YubiHSM Connector are required. KSP integrates the device with the Microsoft Cryptography API: Next Generation – CNG.
In the current YubiHSM KSP implementation, the direct yhusb:// mode is not supported, so the YubiHSM Connector service is used in this implementation.
Applications using PKCS#11
For applications supporting the PKCS#11 standard, the following module is used:
yubihsm_pkcs11
Configuration via the yubihsm_pkcs11.conf file
Possibility of integration with applications and PKI systems using the standard PKCS#11 interface, among others. Example Application
Securing root and intermediate CA keys
Microsoft Active Directory Certificate Services
PKI infrastructure
Code Signing
Certificate Signing
Digital Signatures of Documents and Data
Protecting Encryption Keys
Protecting Application Keys
Protecting IoT Environments
Securing DevOps Infrastructure and Software Development Processes
Protecting Production Processes and the Supply Chain
Securing Keys Used in Cloud Environments
Bring Your Own Key – BYOK in Multi-Cloud Environments
Securing Keys Used by Servers and Applications
Systems Requiring PKCS#11
Environments Requiring Hardware Key Storage
In the YubiHSM 2 FIPS Version – Systems Requiring a FIPS 140-3 Level 3 Module
Manufacturer: Yubico AB
Manufactured in Sweden, USA
Series: YubiHSM 2
Device type: Hardware Security Module - HSM
Physical interface: USB-A
USB interface: USB Full Speed 12 Mbit/s
Port compatibility: USB 1.x / USB 2.0 / USB 3.x via USB-A
Format: Nano
Dimensions: approx. 12 × 13 × 3.1 mm
Weight: approx. 1 g
Average current consumption: approx. 20 mA
Maximum current consumption: approx. 30 mA
Battery: no
Moving parts: no
Water and dust resistance: IP68
Mechanical resistance: crush-resistant
Number of simultaneous sessions: 16
Number of object slots: 256
Maximum total object data space: approx. 128 KB
Supported objects: authentication keys, keys Asymmetric keys, symmetric keys, HMAC keys, Wrap Keys, X.509 certificates, and other binary data
Supported RSA keys: RSA 2048, RSA 3072, RSA 4096
Supported ECC curves include: P-224, P-256, P-384, P-521, and Brainpool
Ed25519 support: yes
ECDSA support: yes
ECDH support: yes
AES support: yes
HMAC support: SHA-1, SHA-256, SHA-384, SHA-512
RSA PKCS#1 support: yes
RSA-PSS support: yes
RSA-OAEP support: yes
Key wrapping: AES-CCM and mechanisms available in firmware 2.4
Integration standard: PKCS#11
Windows integration: Microsoft CNG / YubiHSM Key Storage Provider
Native programming interface: libyubihsm
Python library: available
Local operation: yes, directly via USB
Network operation: yes, using the YubiHSM Connector
Encrypted key backup: yes
M-of-N mechanism configurable for key recovery: yes.
The YubiHSM 2 is a compact hardware security module (HSM) from Yubico designed for securely generating, storing, and using cryptographic keys. The device isolates private keys from the operating system and server applications, enabling cryptographic operations without the need to expose key material outside the protected hardware environment.