- New
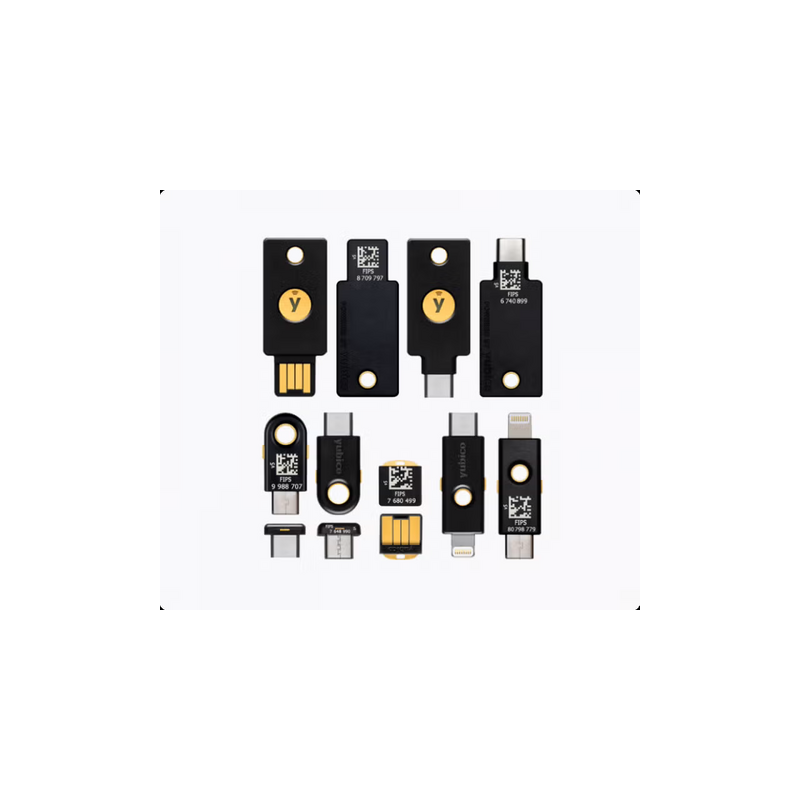
The YubiKey 5 FIPS Series is a professional series of hardware security keys from Yubico, designed primarily for public administration, government institutions, defense, finance, healthcare, and businesses and organizations operating in environments subject to stringent security and compliance requirements.
YubiKey 5 FIPS Series – FIPS 140-3 Certified Hardware Security Key
The YubiKey 5 FIPS Series is a professional series of hardware security keys from Yubico, designed primarily for public administration, government institutions, defense, finance, healthcare, and businesses and organizations operating in environments subject to stringent security and compliance requirements.
The current generation YubiKey 5 FIPS with firmware 5.7.4 is FIPS 140-3 Security Level 2 validated, with Physical Security Level 3, under the CMVP (Cryptographic Module Validation Program) of the National Institute of Standards and Technology (NIST). The series also meets the highest level of authentication assurance (AAL3) specified in NIST SP 800-63B.
The YubiKey 5 FIPS enables phishing-resistant multi-factor authentication (MFA) and passwordless authentication. The keys utilize a hardware-based Secure Element to protect cryptographic keys and support both modern FIDO2/WebAuthn mechanisms and hardware passkeys, as well as solutions used in enterprise infrastructures such as PIV Smart Card, OpenPGP, OATH-TOTP, and OATH-HOTP.
The series is designed to enable the use of a single physical device in modern cloud environments, hybrid systems, and existing infrastructures using certificates and smart cards.
The YubiKey does not require a battery or its own internet connection. Authentication is performed by connecting the device to a USB port or—on applicable models—via NFC or Lightning.
The YubiKey 5 FIPS keys feature an IP68-rated water- and dust-resistant design, no moving parts, and high mechanical durability.
Key Features
FIPS 140-3 Security Level 2 Validation
Physical Security Level 3
Compliance with NIST SP 800-63B AAL3 requirements
Hardware-based, phishing-resistant authentication
MFA support - Multi-Factor Authentication
Passwordless authentication support
Hardware passkey support
FIDO2 and WebAuthn support
PIV Smart Card support
OpenPGP support
OATH-TOTP support
OATH-HOTP support
Challenge-Response support
Yubico OTP support outside the scope of FIPS 140-3 validation
Hardware Secure Element protecting cryptographic material
Suitable for use in government and regulated environments
Suitable for integration with modern and legacy authentication systems
Battery-free
No moving parts
No need to connect the key to Internet
IP68 water and dust resistance
Crush resistance
USB-A, USB-C, NFC, and Lightning models available
Compatible with Windows, macOS, Linux, and ChromeOS
Compatible with popular browsers and services supporting FIDO2/WebAuthn
YubiKey 5 FIPS Series Models/Variants
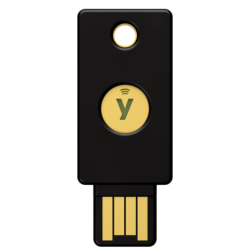
YubiKey 5 NFC FIPS (140-3)
Connector: USB-A
NFC: Yes
NFC standard: ISO/IEC 14443-3 Type A
Dimensions: 18 × 45 × 3.3 mm
Weight: Approx. 3 g
Format: Full-size key
Firmware: 5.7
FIPS 140-3: Yes
Application: USB-A computers and NFC-enabled devices
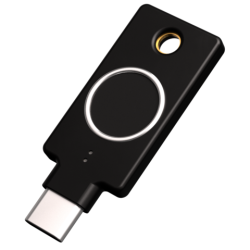
YubiKey 5C NFC FIPS (140-3)
Connector: USB-C
NFC: Yes
NFC standard: ISO/IEC 14443-3 Type A
Dimensions: 18 × 45 × 3.7 mm
Weight: Approx. 4.1 g
Format: Full-size key Key
Firmware: 5.7
FIPS 140-3: Yes
Application: Computers, tablets, and mobile devices with USB-C or NFC
YubiKey 5C FIPS (140-3)
Connector: USB-C
NFC: No
Dimensions: 12.5 × 29.5 × 5 mm
Weight: Approx. 2 g
Format: Compact Key
Firmware: 5.7
FIPS 140-3: Yes
Application: Devices equipped with USB-C
YubiKey 5 Nano FIPS (140-3)
Connector: USB-A
NFC: No
Dimensions: Approx. 12 × 13 × 3.1 mm
Weight: Approx. 2.9 g
Format: Nano
Firmware: 5.7
FIPS 140-3: Yes
Application: Semi-permanent Installation in a USB-A port on a computer or workstation
YubiKey 5C Nano FIPS (140-3)
Connector: USB-C
NFC: no
Dimensions: 12 x 10.1 x 7 mm
Weight: approx. 1 g
Format: Nano
Firmware: 5.7
FIPS 140-3: yes
Application: Semi-permanent installation in a USB-C port on a computer or workstation
YubiKey 5Ci FIPS (140-3)
Connectors: USB-C and Lightning
NFC: no
Dimensions: 12 x 40.3 x 5 mm
Weight: approx. 2.9 g
Firmware: 5.7
FIPS 140-3: yes
Hardware compatibility: including Apple MFi
Application: Devices equipped with USB-C or Lightning
Software Required for Operation
For basic use of the YubiKey 5 FIPS as a FIDO2/WebAuthn key in compatible systems and services, installing a separate driver or a dedicated Yubico app is not required.
In environments utilizing full FIPS functionality, however, device configuration depends on the protocol used.
Yubico Authenticator – recommended graphical tool
Available for computers and mobile devices
Enables OATH authentication
Manages selected key functions
Enables FIDO2, OATH, and PIV applications to be FIPS Approved
Can be used to manage PINs and configure selected functions
YubiKey Manager – ykman CLI
Available for Windows, macOS, and Linux
Required for advanced YubiKey configuration
Enables FIDO2, PIV, OATH, OpenPGP, YubiHSM Auth, and other applications
Enables device function initialization in FIPS Approved mode
Is the official tool used in Yubico documentation to prepare the module for FIPS 140-3 compliance
YubiKey Smart Card Minidriver – optional
System: Windows
Intended for environments using PIV/Smart Card
Can be used, among others, in Together with Microsoft Active Directory Certificate Services and certificate management solutions
PKCS#11 – optional
Used when integrating the YubiKey with applications and systems using the PKCS#11 cryptographic interface
Important Information Regarding FIPS 140-3
Current YubiKey 5 FIPS devices with firmware 5.7.4 are shipped with FIPS Approved mode disabled. Before creating credentials intended for FIPS 140-3 compliance, the relevant key applications must be properly initialized.
Depending on the feature being used, it is necessary to set appropriate PINs, access codes, or management keys, among other things. For FIDO2, a PIN of at least 8 characters is required. Once a feature has been successfully switched to FIPS Approved mode, it cannot be exited without resetting the relevant application.
Therefore, in applications requiring formal FIPS compliance, the device should be implemented in accordance with Yubico documentation and the organization's security policy.
Manufacturer: Yubico AB
Manufactured in: Sweden, USA
Technical Specifications
Manufacturer: Yubico AB / Yubico
Series: YubiKey 5 FIPS Series
Device Type: Hardware Security Key
Current Generation: YubiKey 5 FIPS 140-3
Current Certified Firmware Generation: 5.7.4 / Firmware Series 5.7
NIST Validation: FIPS 140-3
Validation Level: Security Level 2
Physical Security Level: Physical Security Level 3
NIST Authentication Level: AAL3
FIDO2: Yes
WebAuthn: Yes
FIDO CTAP 2.1: Yes
Hardware Passkeys: Yes
Number of Stored FIDO2 Credentials / Passkeys: Up to 100
PIV Smart Card: Yes
Number of PIV Certificates: Up to 24
OpenPGP: Yes
OATH-TOTP: yes
OATH-HOTP: yes
Number of OATH credentials: up to 64
Yubico OTP: hardware-supported; Touch-Triggered OTP is not validated under FIPS 140-3.
Number of OTP seeds: 2
Challenge Response: Yes
Static Password: Yes
FIDO U2F: The device has U2F functionality, however, in FIPS 140-3 compliant mode, U2F is disabled and FIDO2 must be used.
Secure Element: Yes
HID Keyboard: Yes
CCID Smart Card: Yes
FIDO HID: Yes
USB interface: USB 2.0, depending on the model, USB-A or USB-C.
NFC: Depending on the model.
NFC standard: ISO/IEC 14443-3 Type A.
Lightning: YubiKey 5Ci FIPS.
USB transfer rate: up to 12 Mb/s.
Power consumption: less than 150 mW.
Battery: No.
Network connection required by the key: No.
Declared number of USB connection cycles: Over 100. 000
Declared number of write/erase cycles: over 500,000
Operating temperature: 0°C to 40°C
Storage temperature: -20°C to 85°C
MTBF: over 100 years
Water and dust resistance: IP68
Crush resistance: up to 25 N m
Hardware compliance markings: including CE, FCC, UKCA, RoHS
Supported systems: Windows, macOS, Linux, ChromeOS; mobile functionality depends on the model, interface, and application
RSA: up to 4096 bits, with FIPS 140-3 mode imposing additional restrictions on permitted algorithms
ECC: including P-256 and P-384
PKCS#11: supported
PIV Smart Card Minidriver for Windows: available
The YubiKey 5 FIPS Series is a professional series of hardware security keys from Yubico, designed primarily for public administration, government institutions, defense, finance, healthcare, and businesses and organizations operating in environments subject to stringent security and compliance requirements.